A payments dashboard is a valuable target. Whoever controls it can decide where future payments land, create API keys, point webhooks at their own server, or change what customers see at checkout. The controls that protect it fall into three groups: how people sign in, what the dashboard asks for before a sensitive change, and how much each API key is allowed to do.
This post goes through each group as it works on 402pay, what it protects against, and a short list of settings worth changing on day one.
Start with what an attacker would want
On most payment platforms, a stolen dashboard session means a stolen balance: the attacker changes the payout account and waits. 402pay is built so that path doesn't exist in that form. Payments land in a self-custody wallet, and a send from it is signed in the browser with the wallet's encryption password, which 402pay never receives. No API key can move funds at all.
That narrows what an attacker can usefully do with an account, but it doesn't remove it. The changes that matter are:
- Replacing the wallet, so future payments land somewhere else.
- Creating an API key or widening an existing key's access.
- Adding a webhook endpoint, or changing one's URL, to read or spoof payment events.
- Adding a passkey of their own, to keep access after you change your password.
Every control below exists to make one of those harder, slower, or louder.
Passkeys
A passkey is a credential stored by your device or password manager and unlocked with a fingerprint, face, or device PIN. It's bound to the site that created it, so a lookalike page can't phish it, and there's no shared secret on our side to leak. On 402pay, signing in with a passkey counts as both factors: it asks for no password and no code, because the device has already verified you.
Passkeys live in Settings → General. Each one is named after the device or manager that made it, shows when it was added and last used, and can be renamed or removed. Add one on each device you use regularly, so losing a phone doesn't lock you out, and remove any you don't recognize. Adding or removing a passkey sends an email naming it.
Two-step verification
If you sign in with a password (at least 15 characters on 402pay), two-step verification adds a six-digit code from an authenticator app. A stolen or reused password is then not enough on its own. The code is also asked for when you change your password or email, or turn two-step verification off.
Turning it on gives you 10 recovery codes. Each works once in place of a code from your app, and using one sends an email saying how many are left. Store them away from the phone that runs the authenticator, and replace them with Get new codes once you're running low. Turning two-step verification on also signs out your other devices, which is a cheap way to end any session you weren't sure about. Our Support guide walks through setup.
| Measure | Passkey | Password and code |
|---|---|---|
| Phishing | Resistant: tied to the real site | A code can be relayed by a fake page |
| What you carry | Your device or password manager | A password and an authenticator app |
| Backup | A passkey on a second device | 10 single-use recovery codes |
Confirming it's you
Strong sign-in protects the front door. A session left open on a shared computer, or taken from a compromised browser, gets past it. So changes that decide where money goes or who can reach your business ask you to confirm it's you, with a passkey or your password, unless you've signed in or confirmed in the last 15 minutes. That covers:
- Creating, replacing, or deleting the wallet, or changing its encryption password.
- Creating an API key, or giving an existing one more access.
- Adding a webhook endpoint, changing its URL, or rotating its signing secret.
- Adding or removing a passkey, and deleting a business.
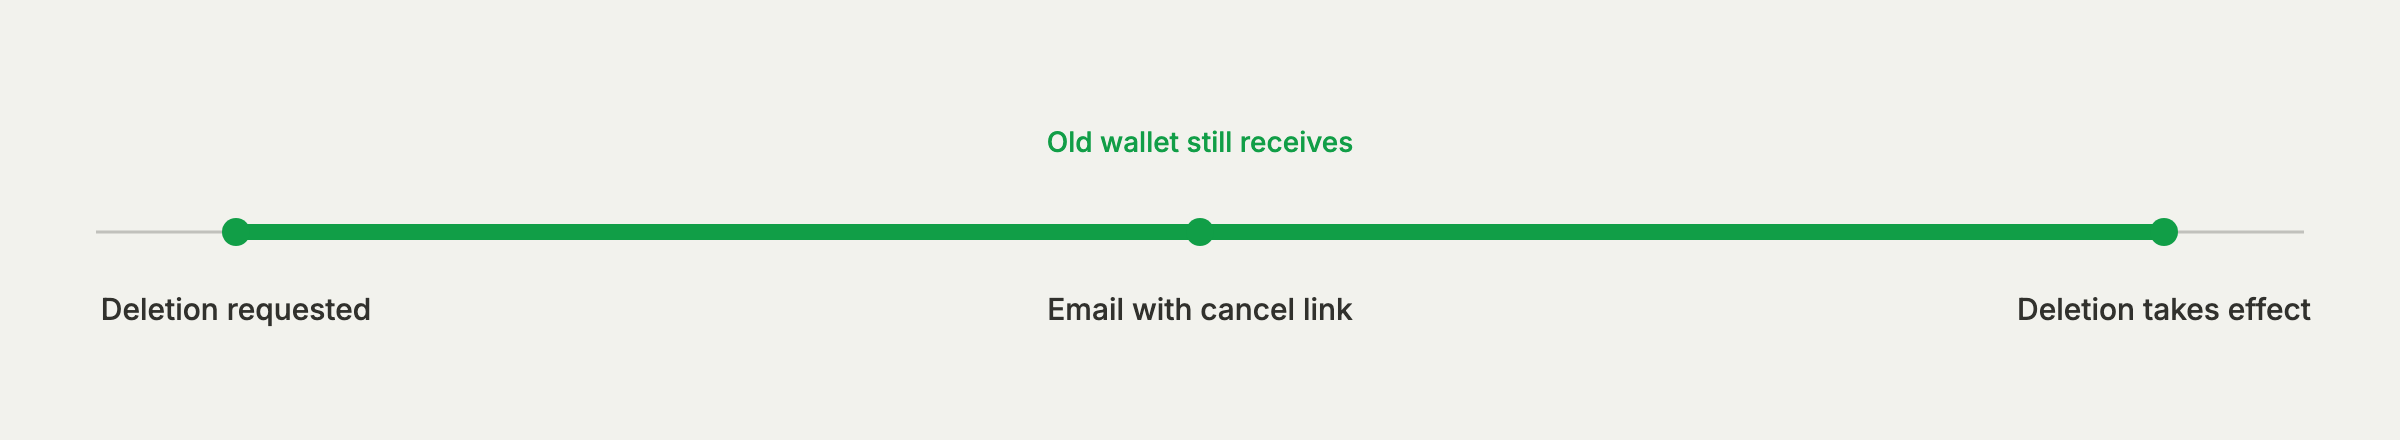
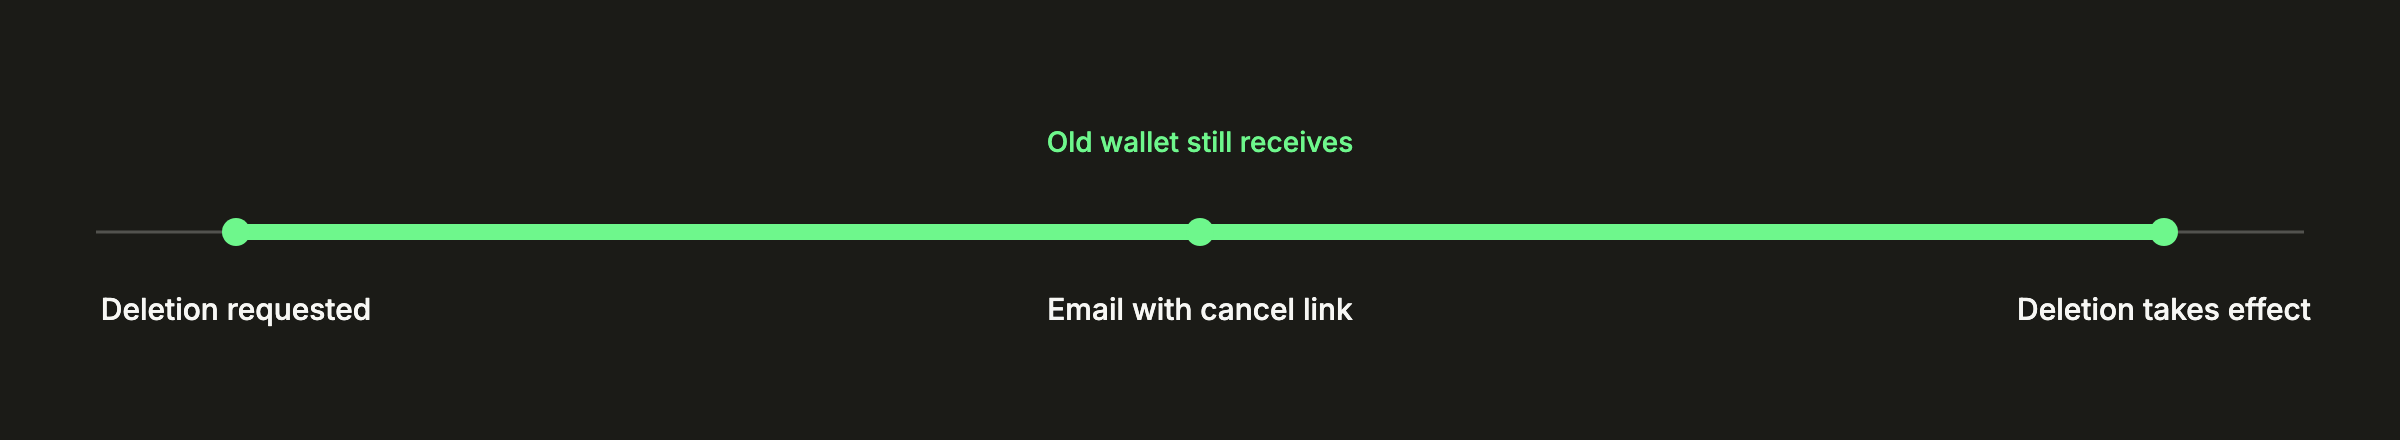
Deleting a wallet that has already received payments has one more safeguard. It takes effect 24 hours after it's requested, the old wallet keeps receiving in the meantime, and the email we send has a link to cancel it. If someone else gets as far as removing your wallet, you have a day to stop it.
Emails you can't turn off
The last line of defense is noticing. 402pay always emails the account's address when something security-relevant happens, and these emails can't be switched off:
| New sign-in | A device and country that hasn't signed in within 90 days, with its location and IP address. |
|---|---|
| Credentials | A password or email change, a passkey added or removed, two-step verification turned on or off. |
| Recovery codes | A code used, or new codes made. |
| Wallet | A wallet added, scheduled for deletion, or deleted. |
If one arrives that you didn't expect, open Settings → General, remove any session you don't recognize, change your password, and check your passkeys. The audit log shows every change people made to the business, who made it, and when.
API keys with scopes
API keys are the other way in, and they tend to end up in more places than anyone intends: CI variables, a contractor's laptop, a log line. A key's secret is shown once and stored only as a hash, so it can't be read back from 402pay. What it can do if it leaks depends on its access.
A Full access key can use everything the API offers for its business. A Restricted key gets None, Read, or Write on each of 7 resources: Payments, Links, Customers, Wallet, Webhooks, Events, and Checkout settings. Reading needs Read; creating or changing anything needs Write. A few examples of what that looks like in practice:
| A store backend | Write on Payments, to create payments and read their status. Nothing else. |
|---|---|
| A reporting job | Read on Payments and Customers. |
| A support tool | Read on Payments, and Write on Customers if agents block customers. |
One key per integration, named after it, makes the list readable and the blast radius small. Each key shows when it was last used, which makes stale keys easy to find. Whatever its access, no key can send funds from the wallet or manage other API keys.
Rotating a key without downtime
Create the new key with the same access, deploy it, then revoke the old one, which stops working at once. See what to do if a secret key leaks. Webhook signing secrets rotate more gently: the old secret keeps signing alongside the new one for 24 hours, so your receivers can switch over without dropping events.
A day-one checklist
None of this takes long. For a new account, in order:
- Add a passkey on your main device, and a second one on another device.
- If you keep a password, turn on two-step verification and store the recovery codes offline.
- Save your wallet's recovery phrase somewhere separate from the computer you sign in on.
- Replace any Full access key with restricted keys, one per integration.
- Verify webhook signatures on every endpoint, and keep signing secrets in your secret store.
- Set your business's support email, so customers reach you rather than their bank.
Make the dangerous changes rare, confirmed, and loud.
For integrations, the developer docs' security best practices cover storing keys and verifying webhooks in more depth.
Common questions
- Yes. You can sign in with a passkey instead of a password, and a passkey sign-in counts as both factors, so it asks for no code.
- Six-digit codes from an authenticator app, with 10 single-use recovery codes as a backup.
- No. Sends are only made in the dashboard and signed in your browser with your encryption password. No API key can make one.
- None, Read, or Write on each of Payments, Links, Customers, Wallet, Webhooks, Events, Checkout settings, with Events limited to Read.
- Changes that decide where money goes or who can reach your business, such as the wallet, API keys, and webhooks, ask for a passkey or your password unless you've signed in or confirmed in the last 15 minutes.
See what 402pay can do for you.
Discover how 402pay helps your business accept any card and get paid in crypto, straight to a wallet you control.